Inside a monorepo
Check Next, Vite and React apps from the workspace root and keep the shared lockfile in step.
PROJECT GOVERNANCE · NEXT.JS / VITE / REACT
Review one policy for every managed app. NKLattice connects inventory, dependency security, code quality, source security, accessibility and browser compatibility to a traceable CI verdict before deployment.
Runs locally · npm & pnpm · Node.js 24+
>=19.3.1>=16.4.2>=8.3.4>=5.9.3The same policy for workspaces and separate repositories
 Next.js
 React
 TypeScript
 Vite
ANONYMIZED PROJECT RESULTS
NKLattice analyzed a private Vite + React codebase. The owner approved publication of these aggregate results; project identifiers and the raw report remain private.
lattice analyze .
NKLattice analyzed 331 modules. Score 11 (F); 232 findings.
Report paths redacted because the source is private.
Static analysis review score for this run; not a runtime or security grade.
lattice governance check . --expect-apps 2
2 applications checked; 5 dependency mismatches.
The policy gate found five mismatches across two discovered package manifests. This run was blocked.
| Manifest | Package | Required | Declared | Locked |
|---|---|---|---|---|
| A | vite | >=6.4.3 | ^5.2.13 | 5.4.21 |
| A | react | >=19.2.0 | ^18.3.1 | 18.3.1 |
| A | react-dom | >=19.2.0 | ^18.3.1 | 18.3.1 |
| B | react | >=19.2.0 | ^18.3.1 | 18.3.1 |
| B | react-dom | >=19.2.0 | ^18.3.1 | 18.3.1 |
Policy failedexit 7
PROJECT GOVERNANCE FOR REACT TEAMS
The source assessment checks each app against a reviewed policy: exact inventory, dependency versions and advisories, architecture, code quality, source security, browser tests and accessibility scans. Every result carries its policy, inventory and input hashes.
PROJECT GOVERNANCE
A passing source assessment means every listed app was found and every required domain had fresh evidence within the reviewed thresholds. Missing scanners, stale evidence and unresolved local imports produce an incomplete result.
Commit the exact app paths and profiles that must be assessed.
.nklattice-apps.jsonSet dependency, architecture, quality, security and compatibility thresholds in the core policy.
governance/policy.jsonThe reusable workflow reports pass, fail or incomplete with JSON and HTML evidence.
needs: governance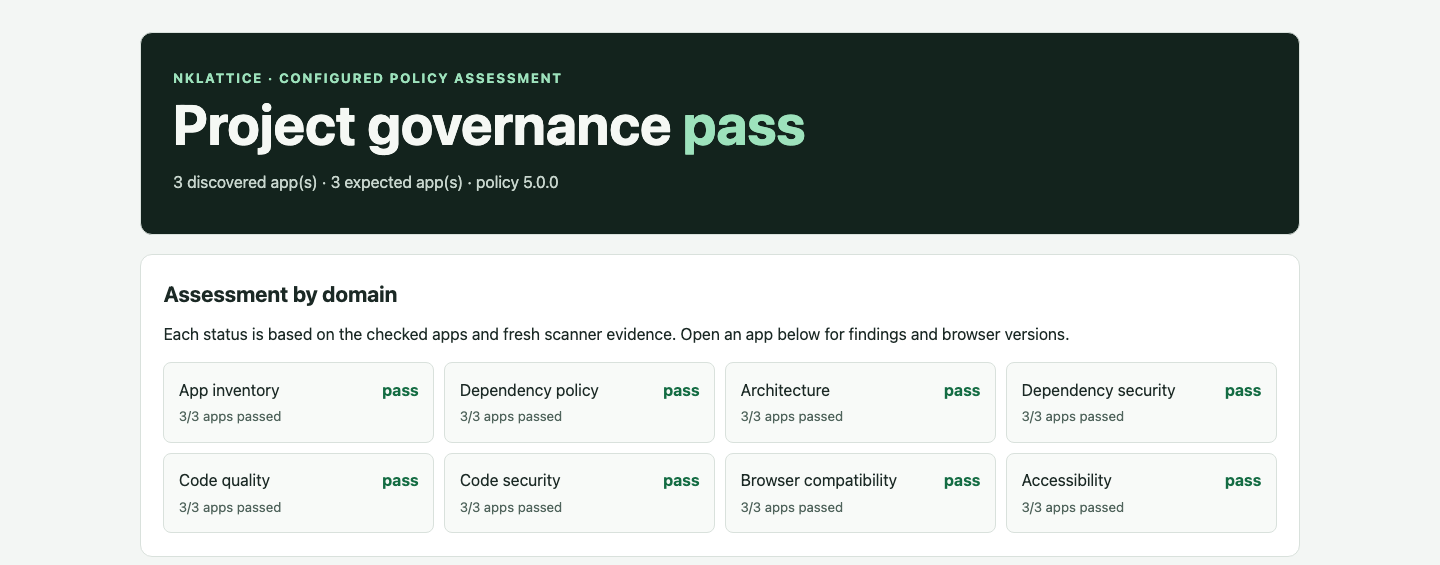
FROM SOURCE TO REPORT
The CLI scans source files, evaluates defined rules and records the evidence behind each finding.
Find supported JavaScript and TypeScript files, excluding dependencies and build output.
Read imports, exports, JSX and file-level structure.
Resolve local imports and connect the modules they reference.
Run configured rules for cycles, boundaries, components and complexity.
Apply category weights and show each deduction behind the review score.
Write an offline HTML report and machine-readable JSON.
governance run executes the required scanners and evaluates their results with inventory, dependency floors and architecture findings in one process. Local analyze remains available for exploration.
See the policy gateARCHITECTURE REPORT
These CLI 0.2.0 screenshots document the private Vite + React run. Project identifiers were replaced before capture; the measured score, counts, category breakdown and selected graph connections were retained. Version 0.5.0 adds a separate eight-domain governance report.
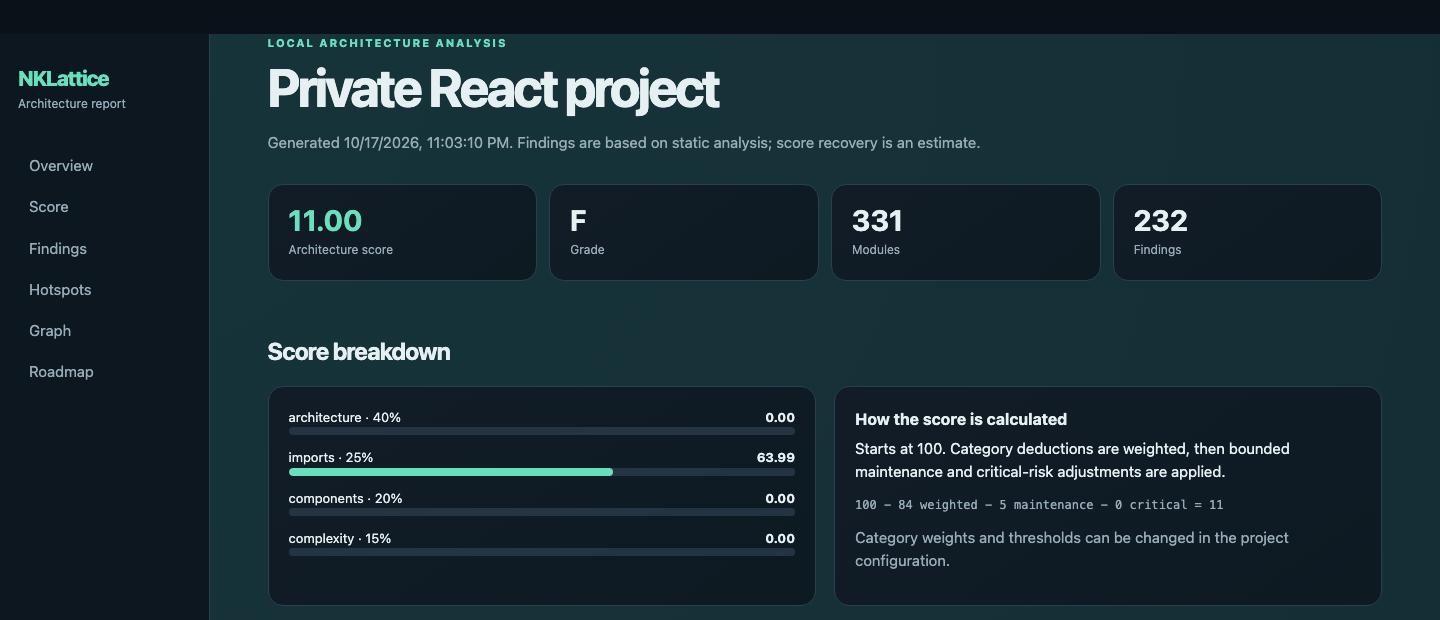
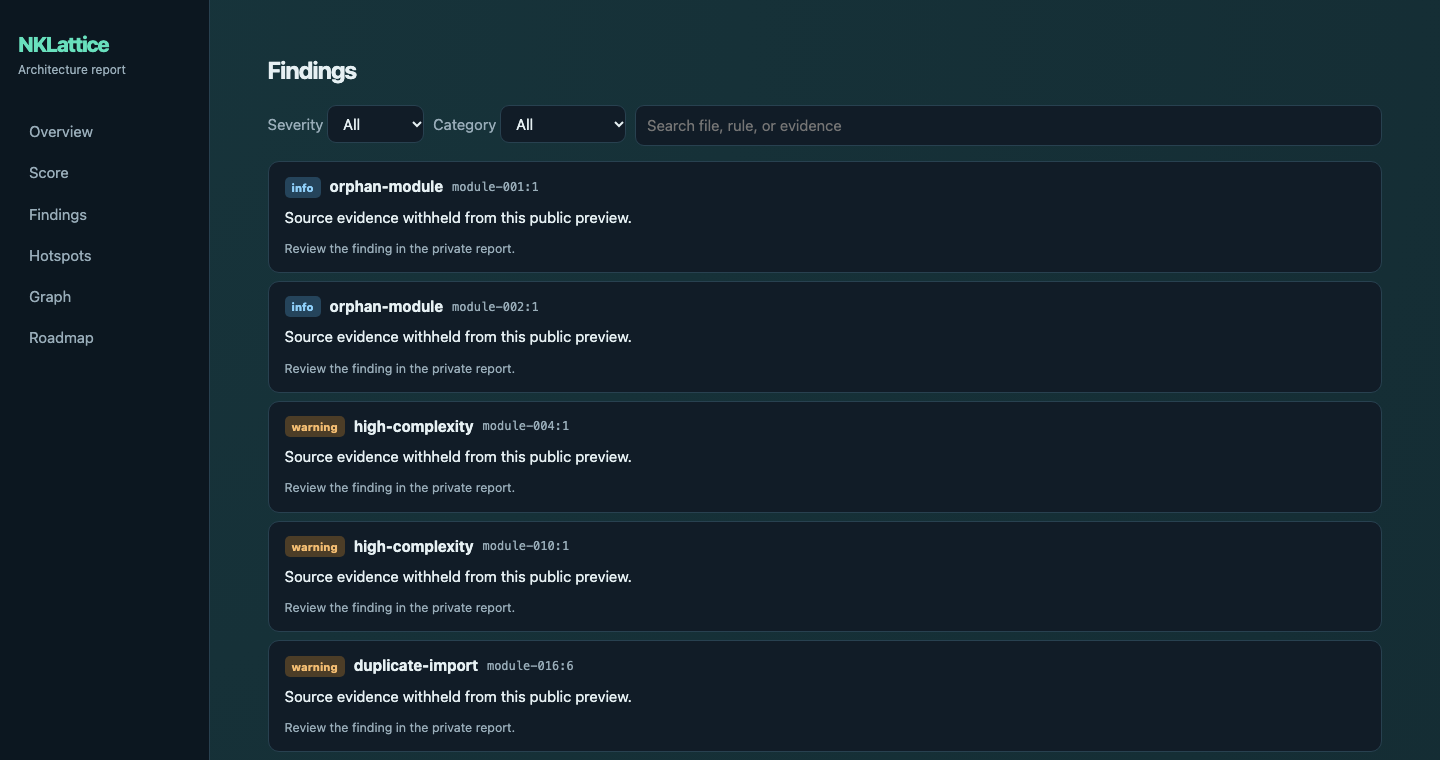
Rule IDs and severities from the analysis; source evidence withheld.
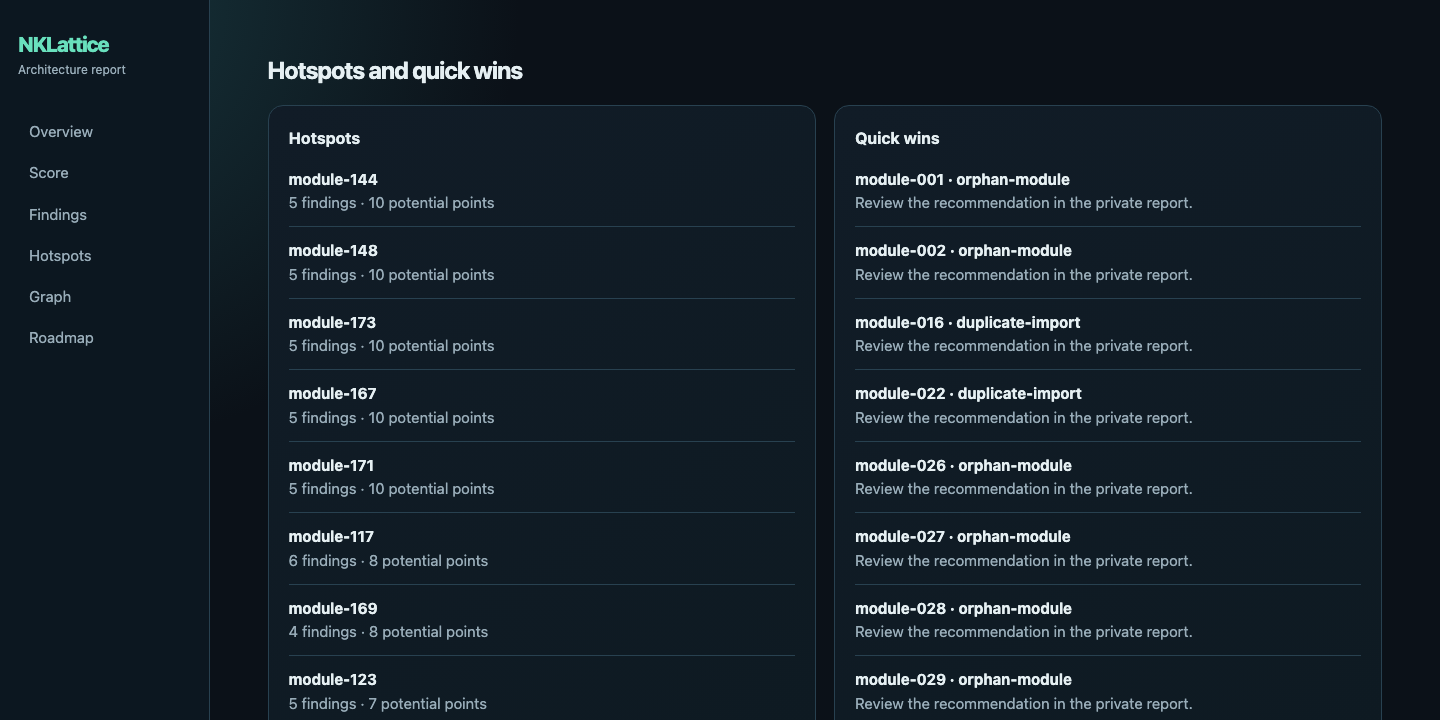
Measured finding counts and estimated impact, with module aliases.
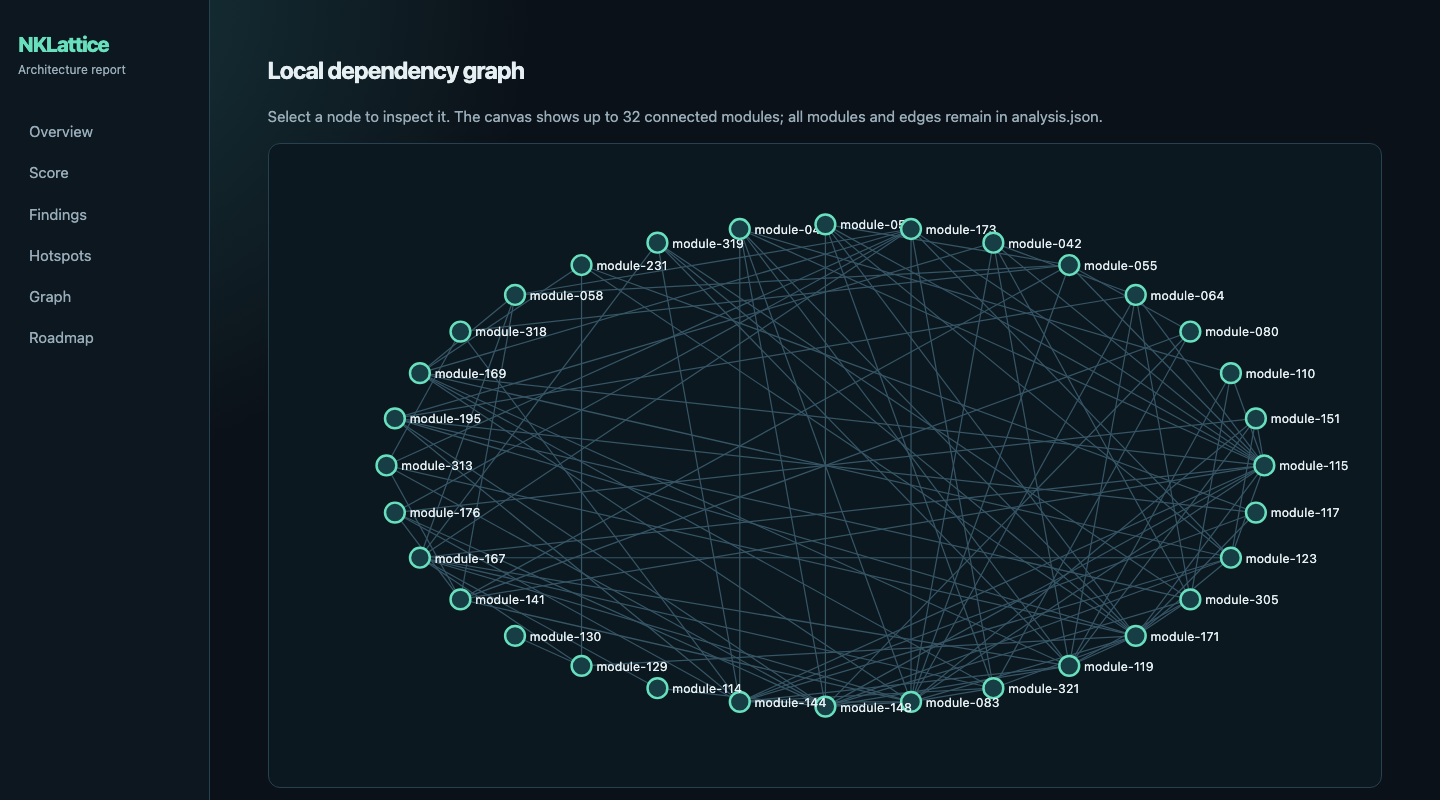
The real selected connections, labeled with module aliases.
MONOREPOS AND STANDALONE APPS
Each repository reviews its app inventory and pins the same central policy revision; workspaces can assess several apps in one run.
Check Next, Vite and React apps from the workspace root and keep the shared lockfile in step.
Each adopted repo pins a core SHA and calls the governance workflow. Its deployment job can wait for that check.
PRODUCT ROADMAP
The eight-domain assessment is available in the CLI. The next proof is a required gate in an independent consumer repository.
Exact inventory, managed libraries, advisories, architecture, quality, security, browser and accessibility evidence by app.
Prove a required governance gate and a deployment dependency in an independent consumer.
Assisted updates, finer architecture rules and comparable reports.
GET STARTED
Review the inventory and policy, run the sample assessment, then make deployment depend on the governance job.