Anonymized React analysis example
The landing page shows owner-approved, anonymized results from a real Vite + React codebase, captured on 17 October 2026 with NKLattice CLI 0.2.0 and policy 2.0.0. The source repository is private. Its name, organization, source paths, and raw report files are not published. The terminal view retains the CLI’s analysis summary and reformats aggregate data from analysis.json; the governance table replaces application paths with A and B.
What the run measured
Section titled “What the run measured”The full checkout scan found 331 supported source modules and 954 resolved internal import links. It produced 232 findings: 169 warnings, 63 informational findings, and no error-severity findings. The score was 11 (F) under the default scoring rules. This is a static-analysis review aid for this scan scope, not a grade for runtime performance, security, or overall product quality. The CLI writes report.html and analysis.json; it exits 0 when analysis findings exist. See Scoring and Reports.
The governance check discovered two managed package manifests: one application root and one nested package that also declares React. Against policy 2.0.0 it reported five mismatches: one Vite, two React, and two React DOM entries. Their declared ranges and locked versions were below the configured minimums. Governance exited 7, so this is a blocked example. It does not demonstrate a passing consumer deployment gate. Review discovery before setting --expect-apps; a nested package can count as a target. See Dependency governance for the separate, reproducible public examples that pass.
Report screenshots and privacy
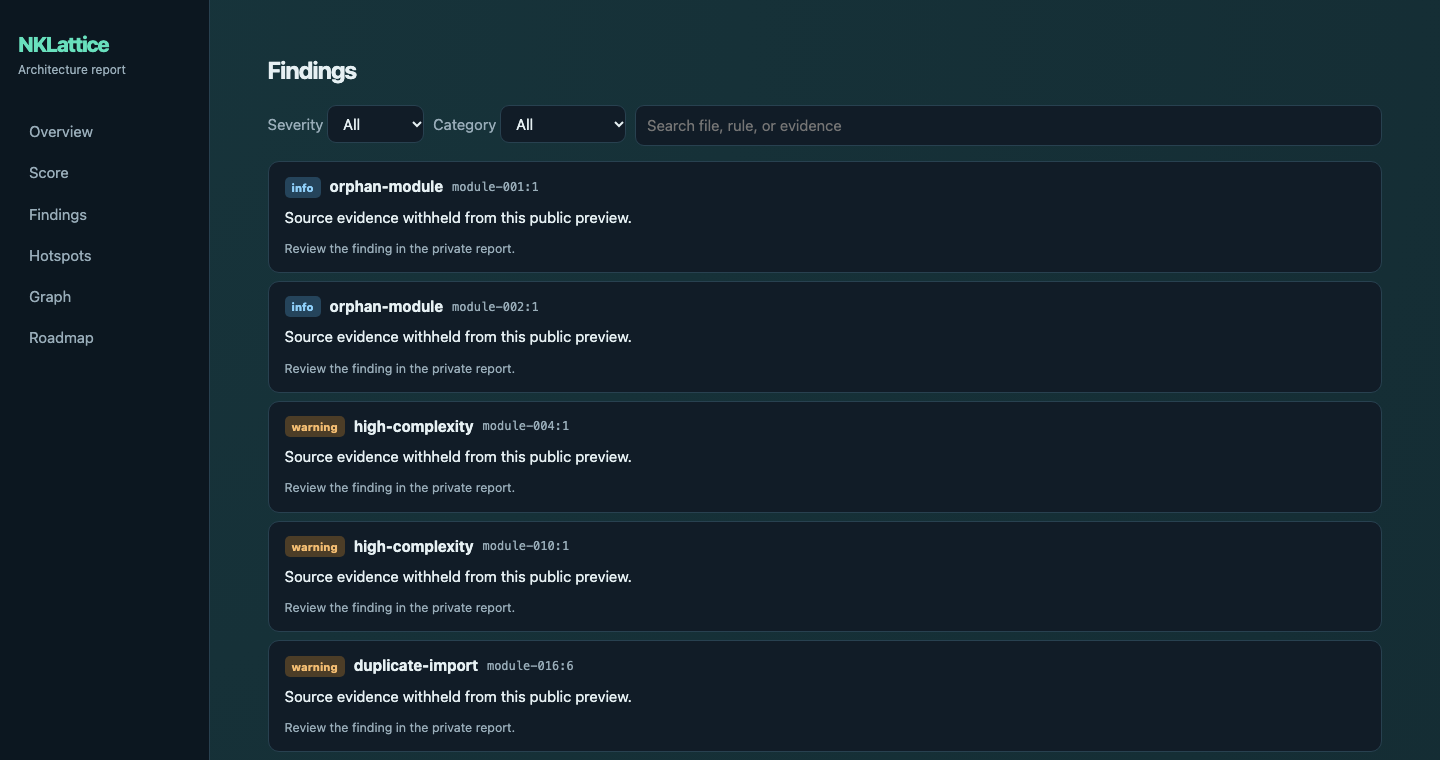
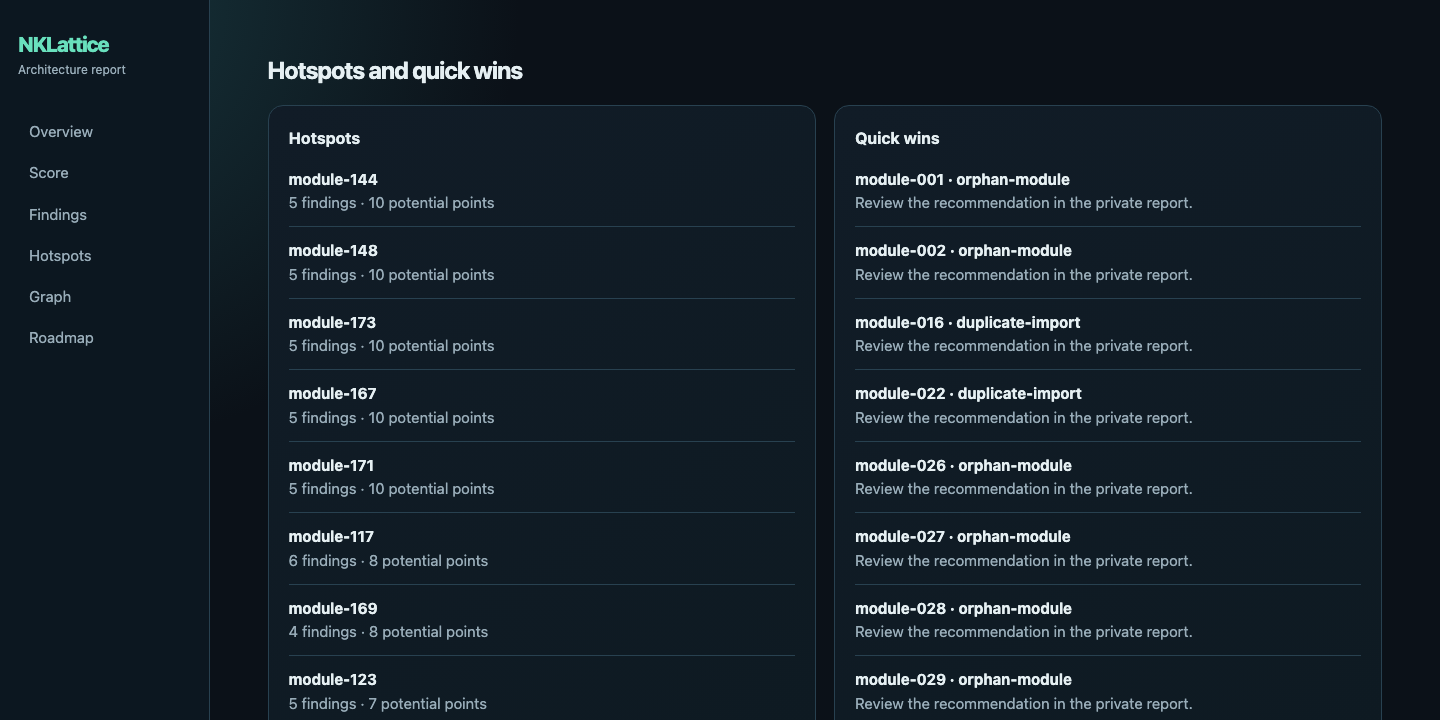
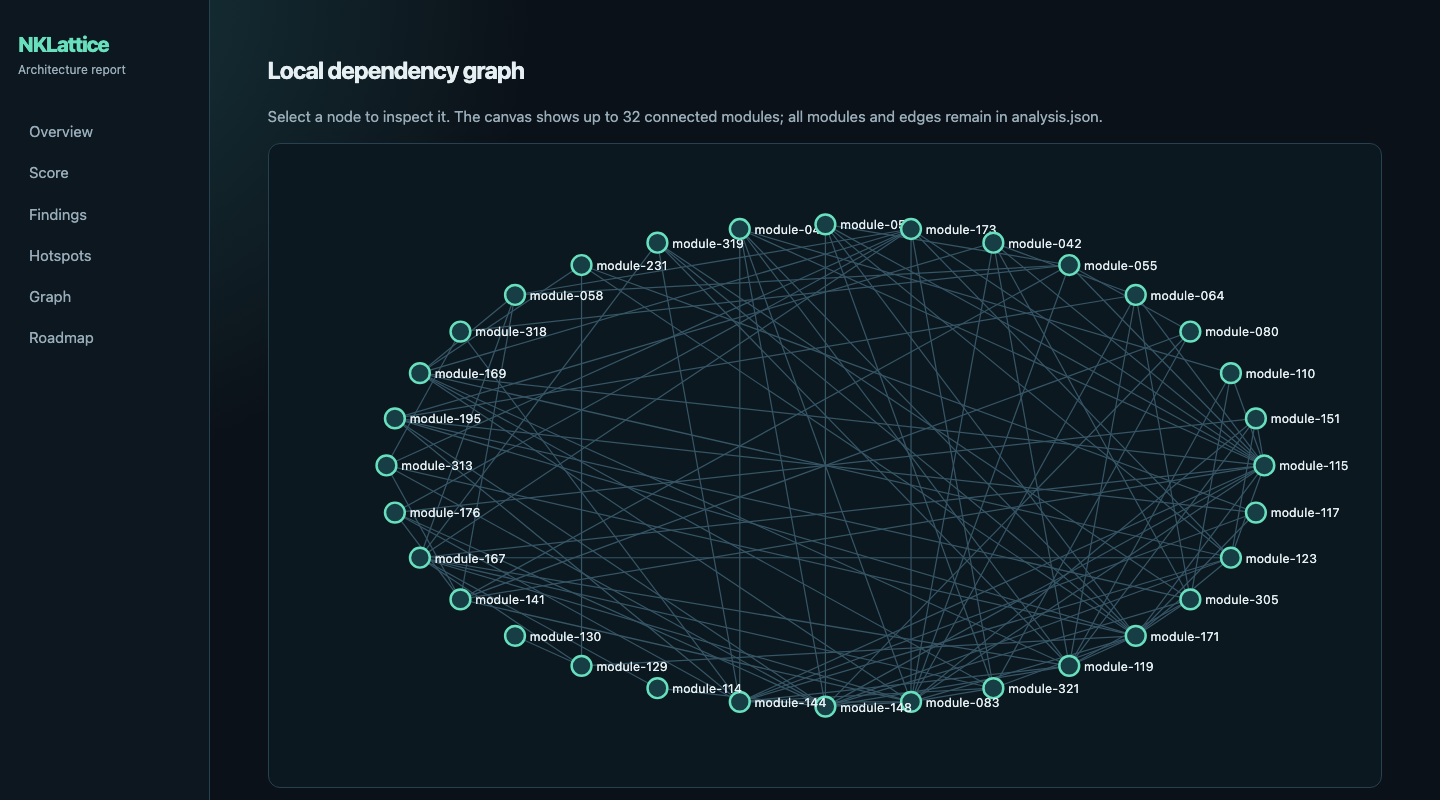
Section titled “Report screenshots and privacy”The landing page shows screenshots from the NKLattice HTML report generated by this run. Before capture, we replaced the project name and source-file paths with generic module aliases. The published images retain the measured score, grade, module and finding counts, category breakdown, finding rule IDs and severities, hotspot counts, and connections in the selected 32-node graph. Source evidence, import names, file names, and recommendations specific to the private codebase are withheld. The raw report and its JSON data remain private.
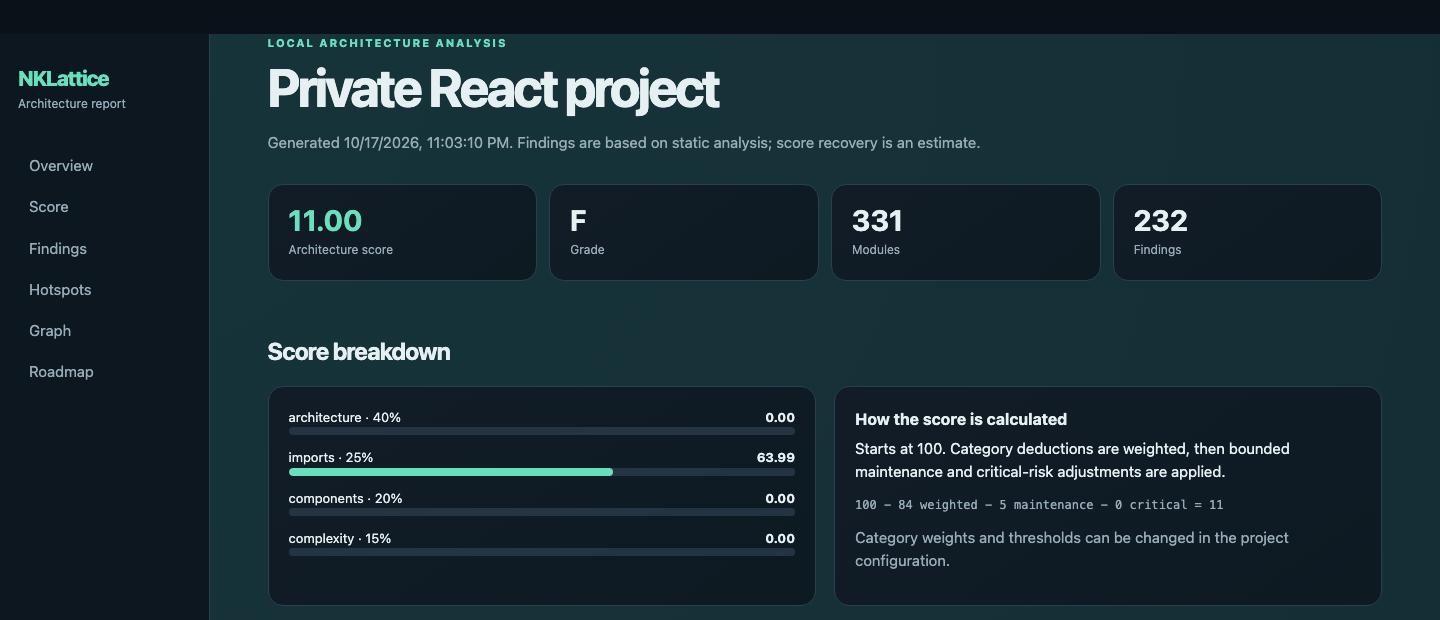
The finding cards, hotspot list, and dependency graph show additional report sections. The graph is a 32-module visual selection; the measured run contains 331 modules and 954 resolved internal import links. A screenshot cannot reproduce the report’s filters or node selection. Run the CLI locally to use those interactions on a repository you control.
Reproduce on your own repository
Section titled “Reproduce on your own repository”Use Node.js 24 or newer and install the exact CLI release in a checkout you control:
npm install --save-dev --save-exact @anhcodo13/lattice@0.2.0npx lattice analyze . --output .nklattice-reportnpx lattice governance check . --expect-apps <number-of-managed-apps> --jsonChoose the expected app count after checking which package manifests match a supported profile. A governance mismatch exits 7 even with --json; a wrong expected count exits 3. Do not upload the raw HTML or JSON report from a private codebase without reviewing project names, paths, findings, and embedded data.
The private run cannot be independently reproduced from this site because its source is not public. For a reproducible public check, use the sample Next, Vite, and React apps and the commands in Quick start.